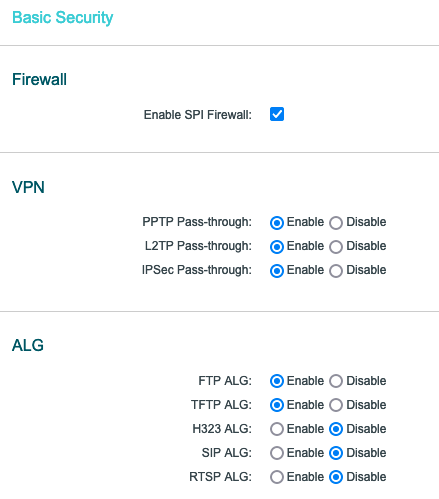
So isn’t that blocking everything except FTP (port 20) and TFTP (port 69)?
Looks like you have found the source of your problems. Except FTP only packets which are answers to requests from inside your local network are allowed to pass from the outside (internet).
So do I need to enabled H323, SIP and RTSP?
It depends what you really want to do. As a first test disable the SPI firewall completely and check if packets gets through afterwards.
Beside the settings shown above: are there other configuration options, where you can selectively configure ports to be excluded from the firewall?
1 Like
No because you’re not trying to use any of those services. If you are trying to set up a web server to serve files over HTTP then you need to enable HTTP or HTTPS ALG (which would be on port 80 or 443 respectively). Or just open up an arbitrary port like 8080 and allow all traffic on that port.
I think “ALG” means it will only allow a specific type of traffic on a specific port, and it will inspect the packets to make sure they are the expected kind of protocol. And it doesn’t seem to have one for HTTP, and you said your ISP blocks port 80 anyway.
Get a new ISP and/or firewall 
These are audio/video session protocols, but won’t help to get standard http requests from the outside through.